I work from Dubai Airport Free Zone, and in the article on fintech I wrote that the region’s rules add up to “constraints that must shape your cloud-region choice before the first line of code, not after.” This article puts UAE regulations for a technology company in one place, across five questions: personal data, cybersecurity, financial regulators, e-invoicing and electronic signatures. It opens a series; next come Saudi Arabia and the rest of the Gulf, the CIS, Russia and Latin America.
On the frame. Everything below comes from primary sources: laws, ministerial decisions, regulators’ rulebooks and their official guidance. Every fact was checked twice: when it was collected, and again by an independent pass against the same document. The check was done on 27–28 September 2026. Some official UAE portals block automated requests, so a few texts were checked against archived copies of the same pages. I do not give legal opinions: the map shows which document to read, and how it applies to your company is a lawyer’s call.
- UAE regulations: four legal regimes in one country
- Personal data: a federal law without the machinery
- Cybersecurity: the obligations sit with government, then flow down to vendors
- Financial sector: what will end up in your contract
- E-invoicing: the nearest deadlines
- Electronic signatures: three levels and an empty register
- Calendar: what changes through 2027
- Where a tech company should start
- What I do not do
- Frequently asked questions
- Is there a personal data protection law in the UAE?
- Do data have to be stored on servers in the UAE?
- When does e-invoicing become mandatory in the UAE?
- Does e-invoicing apply to free-zone companies?
- How quickly must an incident be reported?
- Are foreign electronic signatures recognised in the UAE?
- Does the federal data law apply to a DIFC company?
- Sources
- Need a consultation?
UAE regulations: four legal regimes in one country
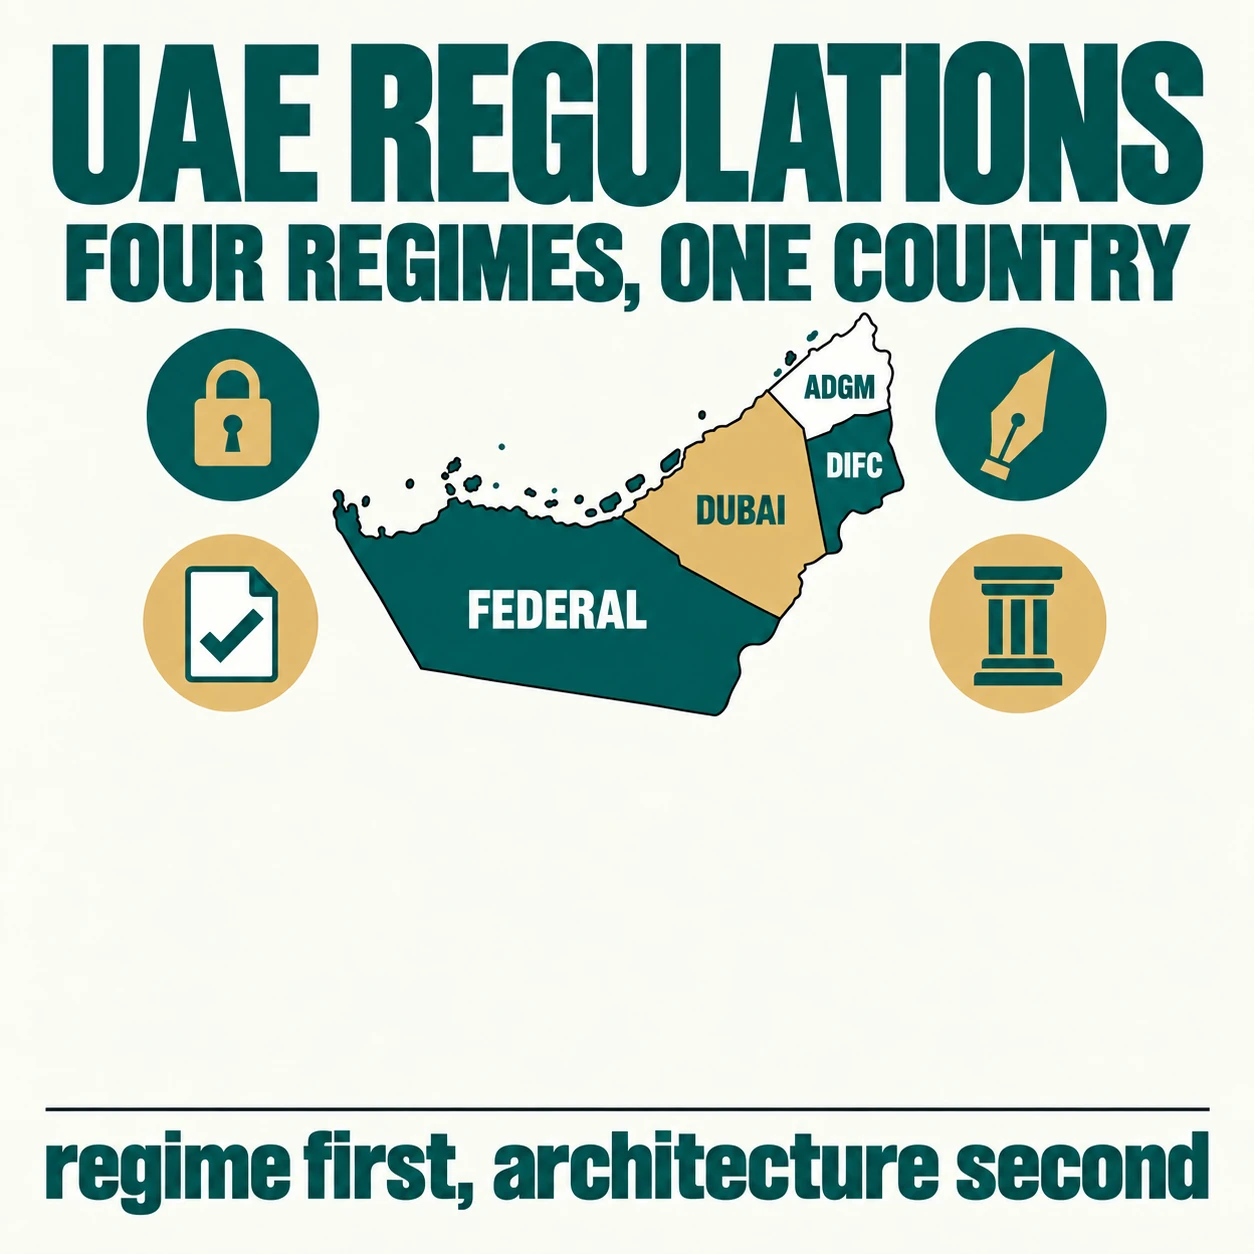
The first thing to understand is that the UAE does not have one rulebook. It has at least four, and which one is yours depends on where your company is registered and who it works with.
- Federal. Federal laws apply across the country, including ordinary free zones.
- Emirate. Emirates have their own laws and bodies. For IT the most visible example is Dubai and its Dubai Electronic Security Center, DESC.
- DIFC in Dubai and ADGM in Abu Dhabi. These are financial free zones. Federal Law No. 8 of 2004 takes them outside federal civil and commercial laws and lets the emirate legislate for them, so they have their own laws on data protection and electronic transactions and their own financial regulators: the DFSA and the FSRA.
That has unexpected consequences. For a DIFC company, the rest of the UAE is legally a “third country”: sending personal data to mainland Dubai or to ADGM counts as a cross-border transfer. And the federal data protection law expressly does not apply to free-zone companies that have their own data protection legislation, as DIFC and ADGM do.
Personal data: a federal law without the machinery
| Regime | Law | Breach notification | Fines |
|---|---|---|---|
| Federal | Federal Decree-Law No. 45 of 2021 (PDPL), in force since 02.01.2022 | To the regulator and the data subject; the deadline is left to executive regulations that do not exist | The Cabinet decision on penalties has not been issued |
| DIFC | DIFC Law No. 5 of 2020, July 2025 consolidation | “As soon as practicable”, no hours set | Up to USD 100,000 per breach, plus a general fine with no cap |
| ADGM | Data Protection Regulations 2021, August 2025 consolidation | Without undue delay, where feasible within 72 hours | Up to USD 28 million |
The federal law. The PDPL has been in force since 2 January 2022 and reaches outside the country: it applies to controllers and processors abroad if they process data of people in the UAE. It does not apply to government data and bodies, to health and banking data that have their own legislation, or to free zones with their own data protection law. The regulator is the UAE Data Office, attached to the Cabinet.
The key fact about this law: its executive regulations still do not exist, although the Cabinet was supposed to issue them within six months, that is, by March 2022. Neither does the Cabinet decision on penalties. According to the latest available copies of the official pages (the law’s entry on the legislation portal as of 27 August 2026, the government portal as of 10 September 2026), neither has been published. In practice that means there are no PDPL fines yet, no fixed breach-notification deadline in hours, and the six-month compliance period, which the law counts from the regulations, has not started. The provisions themselves are published and in force, so it makes sense to build processes around them now: lawful bases, data subject rights, breach notification to the regulator and the data subject, a DPO for high-risk processing, systematic assessment of sensitive data (including profiling) or large-scale sensitive processing. Once the regulations appear there will be up to six months to comply, which the Cabinet may extend by another six. The law has no general registration duty; only the DPO’s contact details go to the Data Office.
Transfers abroad are allowed in cases approved by the Data Office: to countries with data protection legislation and a judicial or regulatory authority that can take measures against the controller, or under an agreement between the UAE and that country. Otherwise the grounds of Article 23 apply: a contract that imposes the law’s requirements, the data subject’s express consent, performance of a contract with them, and others. The Data Office has not published a list of approved countries.
Where data does have to stay in the country. The PDPL has no general localisation rule, but sector rules do. Health data relating to services provided in the UAE may not be stored, processed or transferred abroad without a separate decision of the health authority (Federal Law No. 2 of 2019, Article 13), with fines of AED 500,000 to 700,000. Payment service providers under Central Bank regulation C 15/2021 keep personal and payment data in the UAE, with a backup in a separate location for the five-year retention period.
Children. Since 1 January 2026, Federal Decree-Law No. 26 of 2025 on child digital safety has been in force. Platforms that operate in the UAE or target users in the UAE may not collect or process data of children under 13 unless all the conditions of Article 7 are met: explicit, documented and verifiable parental consent, an easy way to withdraw it, a clear privacy notice, access limited to the minimum, and no commercial use, targeted advertising or tracking. The regulator is the TDRA, and the compliance deadline is 1 January 2027 unless the Cabinet extends it.
DIFC follows a model close to the European one. Controllers and processors register with the Commissioner of Data Protection within 30 days of starting processing and renew every year; the register is public. Fines come in two layers: caps of up to USD 100,000 for individual breaches, and on top of them a general fine with no cap. The right to claim compensation for a breach, including non-material damage, directly in the DIFC Courts already existed (Article 64); since July 2025 it sits in a dedicated Article 64A, a private right of action with rules on how liability is split between controller and processor.
ADGM charges an annual fee of USD 300, expects breach notification within 72 hours where feasible, and requires a DPO where core activities involve regular and systematic monitoring of individuals on a large scale or large-scale processing of special category data. ADGM treats as adequate the jurisdictions recognised by the European Commission and, in the region, DIFC, the QFC and Israel. The maximum fine is USD 28 million.
Cybersecurity: the obligations sit with government, then flow down to vendors
Almost every cybersecurity obligation in the UAE is addressed to government bodies and to critical infrastructure designated by the regulator. A private tech company is usually not in that circle on its own unless the regulator designates it as critical infrastructure: cloud, data centre and DNS providers are named in the sector list. More often it enters through a contract: when its customer is a government body, a critical infrastructure operator or a bank.
Federal level. The regulator is the UAE Cybersecurity Council. The core control standard is the UAE Information Assurance Standard, version 2.1, November 2025. It applies to ministries, federal bodies and non-government critical infrastructure, and in that role it replaced IA Regulation version 1.1, which the TRA issued in 2020. Controls marked “Always Applicable” are mandatory for everyone. The rest also apply unless a risk assessment justifies excluding them, and the justification goes to the Council. Implementation is phased by priorities P1 to P4.
Critical infrastructure reports incidents through sector monitoring centres to the national SOC. For a level 3 incident (medium) the deadline is 60 minutes, for level 4 (low) 1,440 minutes, that is a day, from the moment the incident is declared.
For cloud there is the National Cloud Security Policy, version 2.0, September 2025. It is mandatory for ministries, federal bodies and non-government critical infrastructure as consumers, and for the cloud providers that serve them. It has three tiers: Baseline, Partial Sovereign and Sovereign. Confidential and Restricted data may sit only in Partial Sovereign or Sovereign, anything more sensitive only in Sovereign, and a sovereign cloud cannot be reached from outside the UAE. The provider notifies customers and UAE authorities of confirmed incidents within 24 hours of confirmation at Partial Sovereign and within one hour at Sovereign. The policy expects a set of certifications from providers: ISO/IEC 27001, 27017, 27018 and 22301, SOC 1 and SOC 2 Type II reports, CSA STAR level 2, and a self-assessment against the UAE and Dubai standards.
Separately there is the accreditation programme NCAP, version 2.0. Certification under it is mandatory for government bodies, critical infrastructure entities and providers of cybersecurity, training and audit services to government. The scope section is wider and names everyone who serves the government sector, and section 2.1.1 says a law or a government customer can require certification, including in procurement. Others can take part voluntarily through self-assessment. Only the Cybersecurity Council issues certificates. I could not confirm from a primary source the date from which mandatory certification actually started.
Dubai. Since 10 October 2024, Dubai Law No. 15 of 2024 on DESC has been in force, replacing the 2014 law. It places direct obligations on government bodies and on non-government organisations that DESC designates as critical, including in free zones such as DIFC. Other private companies are covered indirectly: the government body that supervises them sets their protective measures, agrees them with DESC and checks them. Direct subjects must follow DESC standards, report threats, breaches and leaks to DESC immediately, connect to the DESC SOC or a DESC-certified one, and not engage information security firms that DESC has not certified.
For vendors, two DESC documents matter most. The Information Security Regulation is mandatory for all Dubai government entities, including their consultants and contractors. The CSP Security Standard is mandatory for cloud providers serving Dubai government and semi-government organisations: compliance can be demonstrated by certification under an ISO/IEC 27001 scheme, with an annual surveillance audit and recertification every three years.
The transition period under the DESC law was one year and ended on 10 October 2025. The DESC board could extend it for the same period, but I found no extension decision, and even an extended period ended on 10 October 2026. Penalties under this law are to be set by a separate resolution of the Chairman of the Executive Council, and as of late September 2026 it has not been published. The general frame is Dubai Law No. 6 of 2026 on administrative violations, in force since 16 March 2026 and applicable in free zones too: a fine of AED 100 to 1,000,000, doubled for a repeat within a year, up to AED 2,000,000, unless other legislation sets a stricter penalty or a different cap.
Financial sector: what will end up in your contract
If your customer is a bank, an insurer or a payment company, its regulator’s requirements will reach you as contract clauses. Better to know them in advance.
| Regulator | Document | Incident notification | Data |
|---|---|---|---|
| Central Bank of the UAE | Operational Risk Management Regulation C 1/2026, in force since 14.09.2026 | 4 hours for events significantly affecting critical operations, report within 24 hours; high-risk incidents 72 hours | The Master System of Record stays in the UAE |
| DFSA (DIFC) | Rulebook, GEN module, section 5.5, since 01.01.2024 | No later than 72 hours for a material cyber incident | No direct localisation requirement |
| FSRA (ADGM) | Rulebook, GEN module, section 3.5, since 31.01.2026 | Immediately, no later than 24 hours | No hard localisation; supplier country risk is considered |
Central Bank of the UAE. The new Operational Risk Management Regulation C 1/2026 came into force on 14 September 2026, applies to all licensed financial institutions and replaced the 2018 circular. For a vendor it contains five important things. The institution’s Master System of Record is kept in the UAE at all times, including under outsourcing; branches of foreign institutions may, with Central Bank approval, keep an up-to-date copy in the UAE instead. Outsourcing an activity whose failure could significantly affect critical operations needs the Central Bank’s prior non-objection; banks also need one for any material outsourcing under the separate Outsourcing Regulation for Banks (Article 8.1). The contract obliges the vendor to meet Central Bank requests and, where the outsourcing could affect critical operations, to allow Central Bank on-site examinations; where data is shared with subcontractors, these terms must be enforceable against them too. Penetration testing of critical functions is done by an independent external party and reported to the board. Changes material to critical operations or materially affecting customers (migrations and system replacements, for example) need an external expert, notice to the Central Bank with the expert’s report at least 30 calendar days ahead, and its written no-objection before go-live; where one system replaces another, they also need a parallel run of old and new.
DIFC and ADGM. Both regulators require a written cyber risk framework approved by the governing body, annual testing of internet-facing systems, and contract terms for ICT suppliers: notify the firm of cyber incidents, help remediate, and allow compliance checks against cyber security standards (the DFSA also requires the supplier to follow the firm’s cyber security requirements). The rule is wider than classic outsourcing and expressly covers cloud services and server maintenance, and responsibility stays with the firm. Both rulebooks also expressly require multi-factor authentication or equivalent protection for internet-facing systems and for privileged access (DFSA GEN 5.5.9, FSRA GEN 3.5.8). The difference in deadlines is material: the DFSA expects notice within 72 hours, the FSRA within 24. In March 2026 the DFSA consulted on operational resilience rules with a 24-month transition; as of late September they had not been adopted.
E-invoicing: the nearest deadlines
This is where the dates are already close. The basis is Ministry of Finance decisions No. 243 and No. 244 of 2025, the second amended by decision No. 66 of 2026.
Who is in scope. Any person conducting business in the UAE, for every business transaction, regardless of VAT registration and of whether it is established in the UAE. B2B, B2G, G2B and G2G are covered. Transactions with individuals who are not in business (B2C) are excluded until a separate ministerial decision, which as of late September 2026 does not exist. The decision contains no exemption for free zones, and the ministry’s guidelines cover free-zone transactions as one of the in-scope invoice scenarios, with an extra beneficiary field. Separately excluded are, for example, VAT-exempt financial services and international passenger air transport.
| Who | Appoint a provider (ASP) | Mandatory go-live |
|---|---|---|
| Revenue of AED 50 million or more | by 30.10.2026 | 01.01.2027 |
| Revenue below AED 50 million | by 31.03.2027 | 01.07.2027 |
| Government entities | by 31.03.2027 | 01.10.2027 |
Revenue means gross income for the last reporting period per the financial statements. The ASP deadline for large companies has already moved once, from 31 July to 30 October 2026, and on 30 June the ministry called that move final. After 30 October, each month or part of a month without a provider can cost AED 5,000. On 27 September the ministry confirmed that 1 January 2027 is not changing for now. A pilot has been running since 1 July 2026 (participants are invited by the ministry), and from the same date any business may adopt the system voluntarily: penalties do not apply to volunteers until their mandatory date.
How it works. The model is decentralised, a “five-corner” one: the supplier and its provider, the buyer and its provider, while tax data goes in parallel to the Federal Tax Authority (FTA). The providers (Accredited Service Providers) must be certified in the Peppol network, and both sides must appoint one. As of 27 September 2026 the ministry’s register lists 56 accredited providers and 8 in final assessment. The format is XML under the Peppol PINT-AE specification, with no QR code. A tax e-invoice has 51 mandatory fields, a commercial one 49. Commercial invoices become electronic too, and PDF or paper does not replace an e-invoice.
Deadlines and penalties. An invoice is issued and transmitted within 14 days of the transaction date or of receiving payment, whichever is earlier; for VAT payers the VAT law’s deadlines take priority. A system failure must be reported to the FTA within two business days. Cabinet Decision No. 106 of 2025 sets the penalties: AED 5,000 for each month of non-implementation, including failing to appoint a provider on time; AED 100 for each invoice or credit note not issued and transmitted on time, capped at AED 5,000 per calendar month; AED 1,000 for each day a failure is not reported.
Retention. Decision No. 243 requires invoices to be kept “within the State”, but the ministry’s guidelines read that as availability to the FTA regardless of where the servers are. Retention is five years, seven for real estate, plus four years in case of a dispute or audit.
For a tech company this raises two questions. The first is about your own billing: can your system issue invoices through a provider in PINT-AE format by your date. The second is about your product: if you build accounting or ERP software for UAE companies, your customers will ask about this before the tax authority does.
Electronic signatures: three levels and an empty register
Federal level. Federal Decree-Law No. 46 of 2021 on Electronic Transactions and Trust Services has been in force since 2 January 2022, with its executive regulation, Cabinet Resolution No. 28 of 2023. The regulator is the TDRA. A signature can be simple, reliable or qualified, and electronic seals have the same levels. A qualified signature equals a handwritten one. Any form of signature may be used unless the law requires otherwise, and government bodies must accept signatures at the trust levels set by the TDRA.
Qualified certificates are issued only by providers with qualified status from the TDRA, and their list is published in the UAE Trusted List. This is the most surprising finding: the machine-readable list issued on 18 December 2025 contains no providers at all. The next issue was scheduled for 17 June 2026, but on 28 September the same empty list was still current. The law recognises foreign qualified services at a comparable level (Article 37), but the TDRA has only outlined the approach (its own assessment of the foreign provider and future mutual recognition agreements) and has published neither a procedure nor any concluded agreement.
For individuals, signing is built into UAE PASS. According to the operator’s documentation only verified accounts can sign: the second verification level gives an Advanced signature, the third, with biometrics, a Qualified one. UAE PASS is not listed in the TDRA register.
Dubai has had no electronic transactions law of its own since 2022, and the federal one applies. Dubai Law No. 9 of 2022 on digital services adds that steps a customer takes through digital channels to obtain digital services under that law count as done in person; the law applies in phases set by the Chairman of the Executive Council. DESC runs Dubai’s public key infrastructure and the Ethaq Plus service for the private sector through its partners.
DIFC is technology-neutral: a signature is valid if it is as reliable as is appropriate for the purpose of the document. Exclusions: powers of attorney, declarations of trust, wills and affidavits for the DIFC Courts. The DIFC legal database tags this law “Inactive”, but it puts the same tag on laws that are plainly in force, such as the Data Protection Law 2020 and the Employment Law 2019, so the tag does not mean repeal. ADGM is technology-neutral too, but expressly recognises signatures created outside ADGM and the UAE and allows remote witnessing of a signature over video. Exclusions: powers of attorney, wills, real estate transactions and notarial documents.
Calendar: what changes through 2027
- 14.09.2026: the Central Bank’s Operational Risk Management Regulation C 1/2026 came into force.
- 10.10.2026: the extended transition under the DESC law ended, if it was extended (I found no extension decision).
- 30.10.2026: deadline for companies with revenue of AED 50 million or more to appoint an e-invoicing provider; after it, AED 5,000 for each month or part of a month of delay.
- 01.01.2027: mandatory e-invoicing for revenue of AED 50 million or more; compliance deadline under the child digital safety law.
- 31.03.2027: companies with revenue below AED 50 million and government entities appoint providers.
- 01.07.2027: mandatory e-invoicing for revenue below AED 50 million.
- 01.10.2027: mandatory e-invoicing for government entities.
- No date announced: PDPL executive regulations and penalties, penalties under the DESC law, B2C e-invoicing.
Where a tech company should start
- Work out your regime. Federal, DIFC or ADGM, and separately your customers’ regimes: they may differ from yours.
- Map your data flows. Which data about people in the UAE you process, where it sits and where it goes. For a DIFC company that includes transfers outside the DIFC, even to mainland Dubai.
- Check sector localisation. Health data, payment service data and financial institutions’ Master System of Record follow their own rules, and there storage in the country is mandatory.
- Understand who will bring cyber rules to you. A government customer, a critical infrastructure operator or a bank will bring standards, certification and notification deadlines into the contract.
- Put e-invoicing in the plan. The revenue threshold sets your date, and appointing a provider and reworking billing take time.
- Pick the signature for the job. The law allows any form of signature unless another law requires a specific one. Where a qualified signature is needed, keep in mind that as of 28 September 2026 the provider register was empty: the TDRA only opened online licence applications on 21 April 2026.
What I do not do
- I do not give legal opinions. I show which document and which article bear on your architecture; how they apply to a specific company is for a lawyer to judge.
- I do not retell secondary sources. Consultants’ overviews are useful as pointers, but every fact here was checked against the text of the law or the regulator’s document.
- I do not promise the map will not age. It holds many dates that have not arrived and decisions that have not been made. Reread it before you decide anything.
Frequently asked questions
Is there a personal data protection law in the UAE?
Yes, Federal Decree-Law No. 45 of 2021 has been in force since 2 January 2022. But as of late September 2026 its executive regulations and the decision on penalties have not been issued, so there are no fines and no fixed breach-notification deadline yet.
Do data have to be stored on servers in the UAE?
The federal data protection law has no general requirement. Mandatory in-country storage exists in specific areas: health data, payment service data, the Master System of Record of financial institutions, and, for ministries, federal authorities and critical infrastructure, data classified Confidential/Restricted and above, which must sit in sovereign cloud tiers hosted in the UAE.
When does e-invoicing become mandatory in the UAE?
From 1 January 2027 for companies with revenue of AED 50 million or more, which must appoint a provider by 30 October 2026. From 1 July 2027 for the rest, with a provider appointed by 31 March 2027. Government entities follow from 1 October 2027.
Does e-invoicing apply to free-zone companies?
The Ministry of Finance decision contains no free-zone exemption: it applies to any person conducting business in the UAE. Free zones are not named in it directly, but the ministry’s guidelines cover transactions with them as one of the in-scope invoice scenarios, with an extra beneficiary field.
How quickly must an incident be reported?
It depends on the regime. Financial institutions supervised by the Central Bank notify it within 4 hours of an event that significantly affects critical operations and within 72 hours of a high-risk incident. FSRA-authorised firms in ADGM report a material cyber incident within 24 hours, DFSA-authorised firms in DIFC within 72 hours. For a personal data breach, ADGM expects notice within 72 hours where feasible, while the federal law has not set a deadline yet.
Are foreign electronic signatures recognised in the UAE?
The federal law recognises foreign qualified services at a comparable level, but the TDRA has only outlined the approach (its own assessment of the foreign provider and future mutual recognition agreements) and has published neither a procedure nor any concluded agreement. In ADGM, signatures created outside ADGM and the UAE expressly have legal effect.
Does the federal data law apply to a DIFC company?
No, DIFC has its own data protection law. But for DIFC the rest of the UAE counts as a third country, so sending data to mainland Dubai follows the cross-border transfer rules. ADGM is formally a third country too, but the DIFC Commissioner of Data Protection lists it as adequate, so transfers there need no additional safeguards.
Sources
- Federal Decree-Law No. 45 of 2021 on Personal Data Protection, UAE legislation portal.
- Data protection laws, UAE government portal.
- Federal Law No. 2 of 2019 on ICT in health fields.
- UAE Information Assurance Standard, UAE Cybersecurity Council (archived copy).
- Dubai Law No. 15 of 2024 concerning DESC, Dubai legislation portal.
- DESC standards and policies and DESC certifications.
- Operational Risk Management Regulation C 1/2026, Central Bank of the UAE.
- Outsourcing Regulation for Banks, Article 8, Central Bank of the UAE.
- Retail Payment Services and Card Schemes Regulation C 15/2021, Article 14.
- DFSA Rulebook, GEN 5.5 and the FSRA cyber risk rules.
- DIFC Data Protection Law No. 5 of 2020 and ADGM Data Protection Regulations 2021.
- Ministerial Decision No. 243 of 2025 and UAE Electronic Invoicing Guidelines, version 1.1.
- Register of accredited e-invoicing service providers, UAE Ministry of Finance.
- Cabinet Decision No. 106 of 2025 on penalties.
- Federal Decree-Law No. 46 of 2021 on Electronic Transactions and Trust Services.
- UAE Trusted List, the machine-readable register of trust service providers.
- ADGM Electronic Transactions Regulations 2021.
Need a consultation?
If you are entering the UAE or working with banks and government customers here, book a call. We start with which regimes apply to your company and your customers, and which of them should shape the architecture. How I work with companies in Dubai is described in the article on a fractional CTO in Dubai.